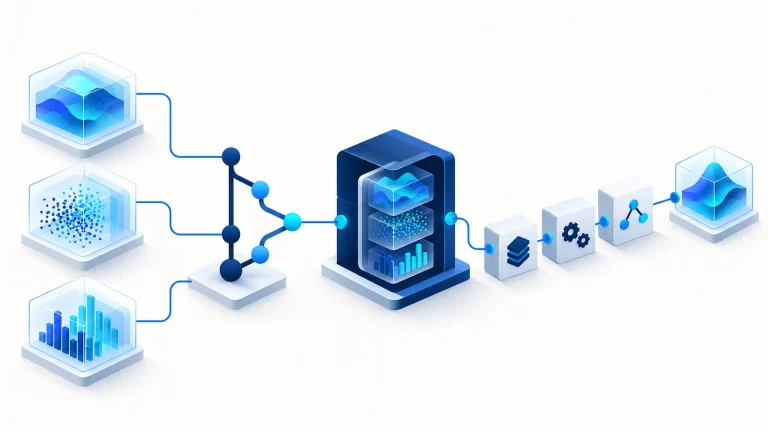
Azure OpenAI, LangChain, Chroma and Chainlit address different responsibilities in a conversational application. Azure provides model access, LangChain supports application composition, Chroma supports retrieval and Chainlit supplies a conversational interface. They are complementary components rather than interchangeable platforms.
Combining them does not automatically produce a secure or reliable assistant. The architecture must define identity, document permissions, evidence selection, model invocation and response handling. Each component creates an operational boundary that needs an owner and a failure strategy.
Separate the four responsibilities
Model access is responsible for sending a request to a chosen deployment and receiving its result. Orchestration prepares inputs and connects processing steps. Retrieval selects relevant stored material. The interface receives user interaction and displays results. Keeping these roles distinct makes integration failures easier to diagnose.
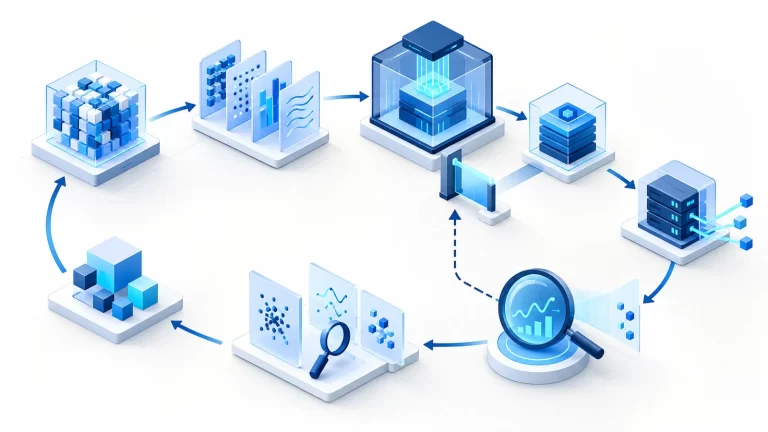
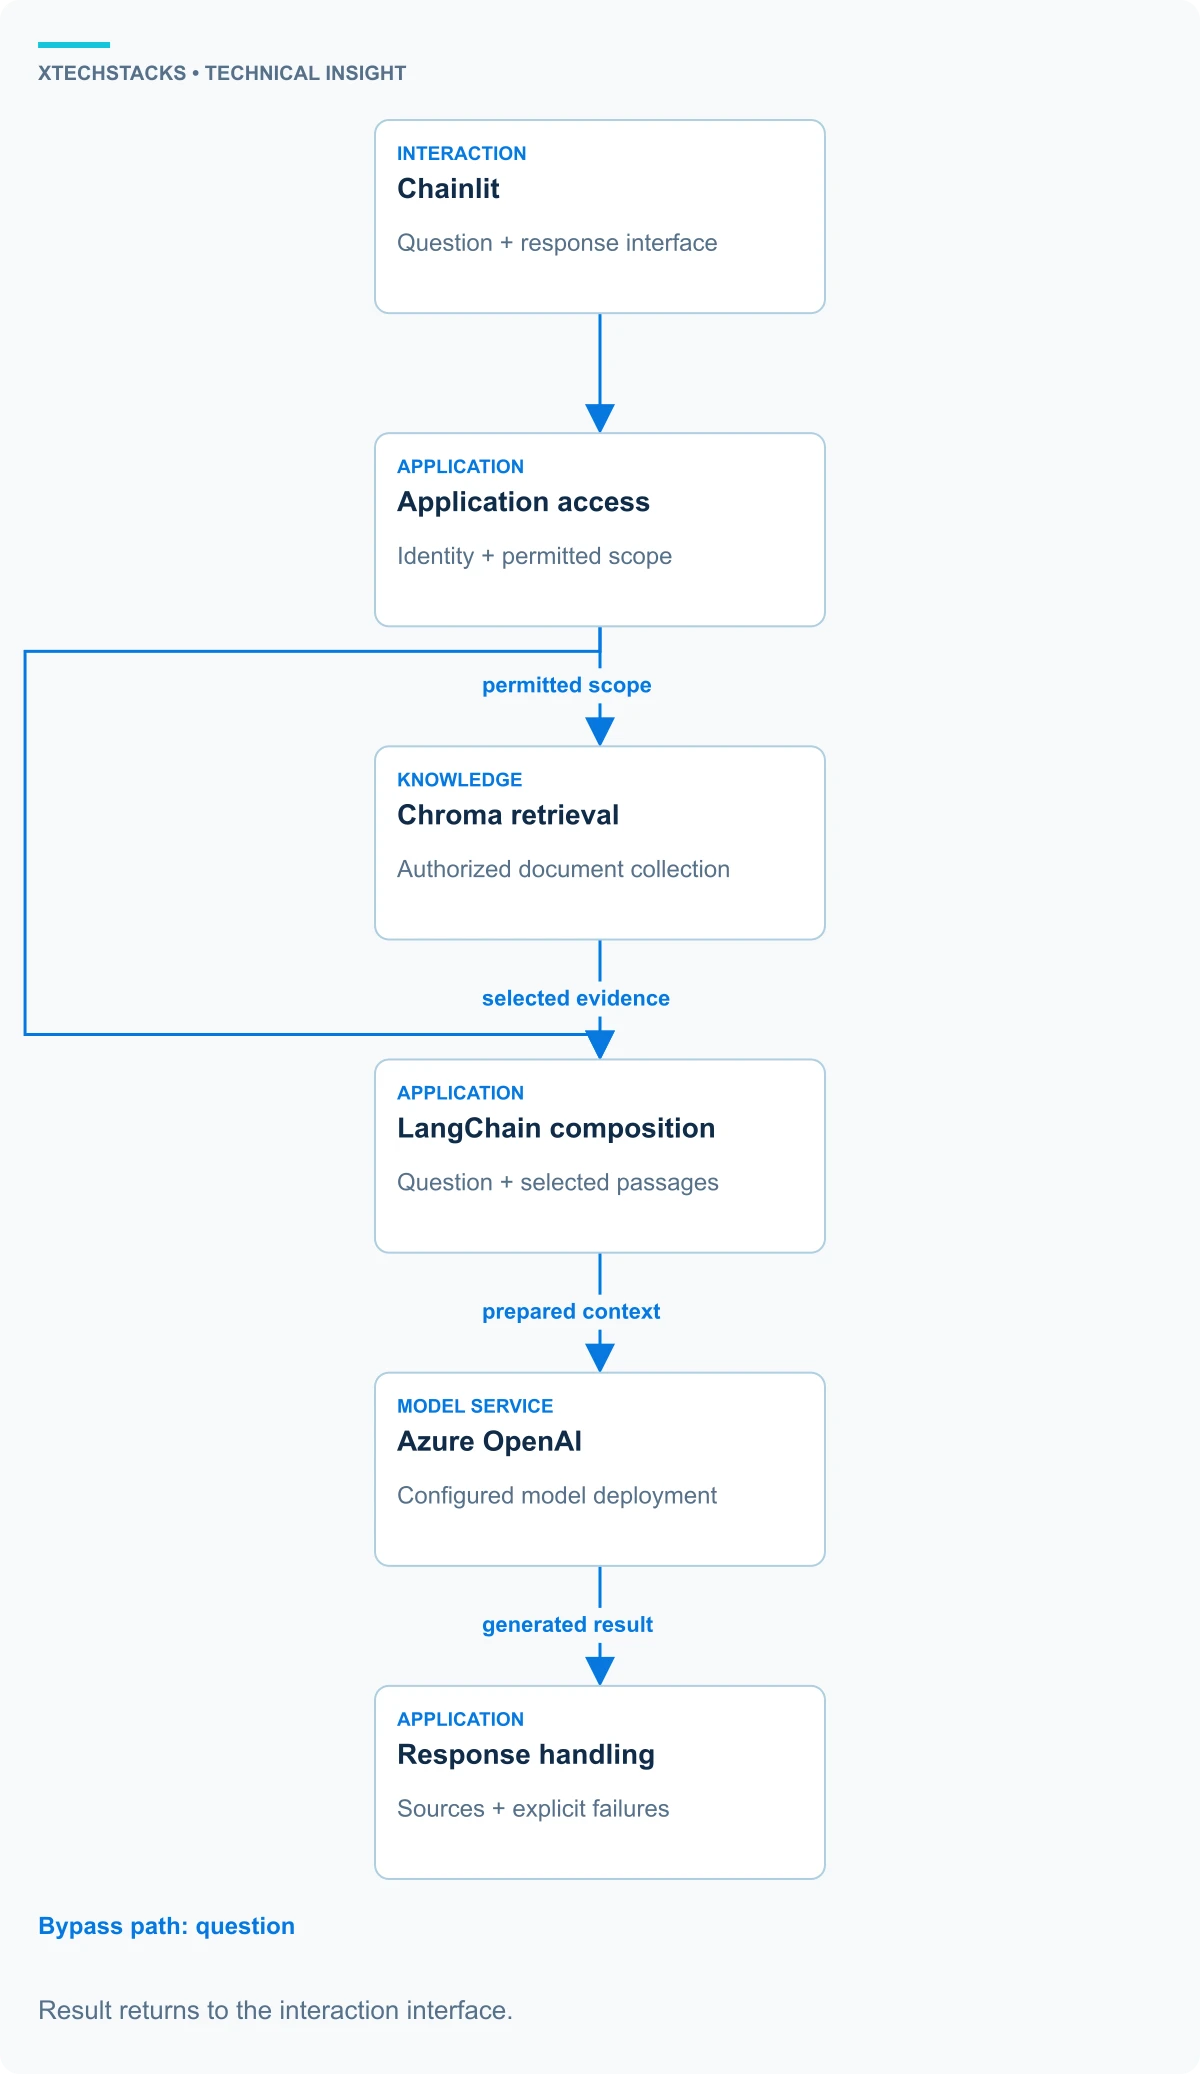
For a hypothetical internal documentation assistant, a user asks a question through Chainlit. Application code establishes identity and access. Retrieval queries an authorized document collection in Chroma. LangChain components can compose retrieval and prompt preparation. The model deployment receives the prepared context and produces a response for review.
Azure OpenAI: managed model access
Azure OpenAI models are available through Microsoft’s managed model offerings. Supported models, deployment types, quotas and regional availability vary. Verify the selected deployment and current service documentation rather than assuming a model is available everywhere or that capacity is unlimited.
Protect credentials or supported service identities, configure appropriate network access and handle provider failures. Set timeouts and request limits. A managed endpoint removes some model-infrastructure work, but the application still owns data transmission, error behavior and evaluation of generated results.
LangChain: composition and integrations
LangChain offers components and interfaces for building model applications. Prompt preparation, runnable composition and retrieval integrations can reduce repetitive glue code. Those abstractions still need explicit input/output contracts and compatible dependency versions.
The trade-off is another dependency layer. For a small application with one model call, direct SDK use may be simpler. Choose a framework because its interfaces solve a concrete composition problem, not because it appears in a reference architecture. Business permissions should remain enforceable in ordinary application code.
Chroma: document and embedding retrieval
Chroma provides storage and search capabilities for documents and embeddings. A retrieval application also needs an ingestion process, chunking rules, document identities and a refresh or deletion strategy. Similarity search selects candidates; it does not establish that their contents are current, correct or authorized for a user.
Evaluate retrieval on representative questions and known missing-information cases. Test how collections are isolated and how permission changes propagate. Rebuilding an index may change answer behavior even when the model and prompt stay unchanged, so preserve index and retrieval configuration in release records.
Chainlit: the interaction layer
Chainlit supports conversational interfaces and integration points such as authentication and persistence. The application must configure those integrations and verify their behavior. An interface package does not inherently provide tenant isolation, safe tool execution or complete security controls.
Display source references and clear failure messages where the application supports them. Avoid exposing internal exception details or credentials to the user. If conversation history is retained, define who can access it, where it is stored and how deletion requests or retention limits are handled.
Container deployment boundaries
Containers can package the interface and application dependencies. Decide separately where persistent retrieval data lives and how it is backed up. An ephemeral application filesystem is not a substitute for deliberate persistence. Validate connection recovery when an instance restarts or scales.
Separate environment configuration from the image and avoid embedding secrets. Define health checks, resource limits and controlled release procedures. Containerization does not demonstrate acceptable answer quality; retain the same evaluation gate for changes to code, prompts, indexes and model configuration.
Implementation sequence
First build a bounded request path with identity, one approved document source and explicit unsupported behavior. Test retrieval independently, then prompt preparation, then model invocation. Add the interface after the backend failure behavior is understandable.
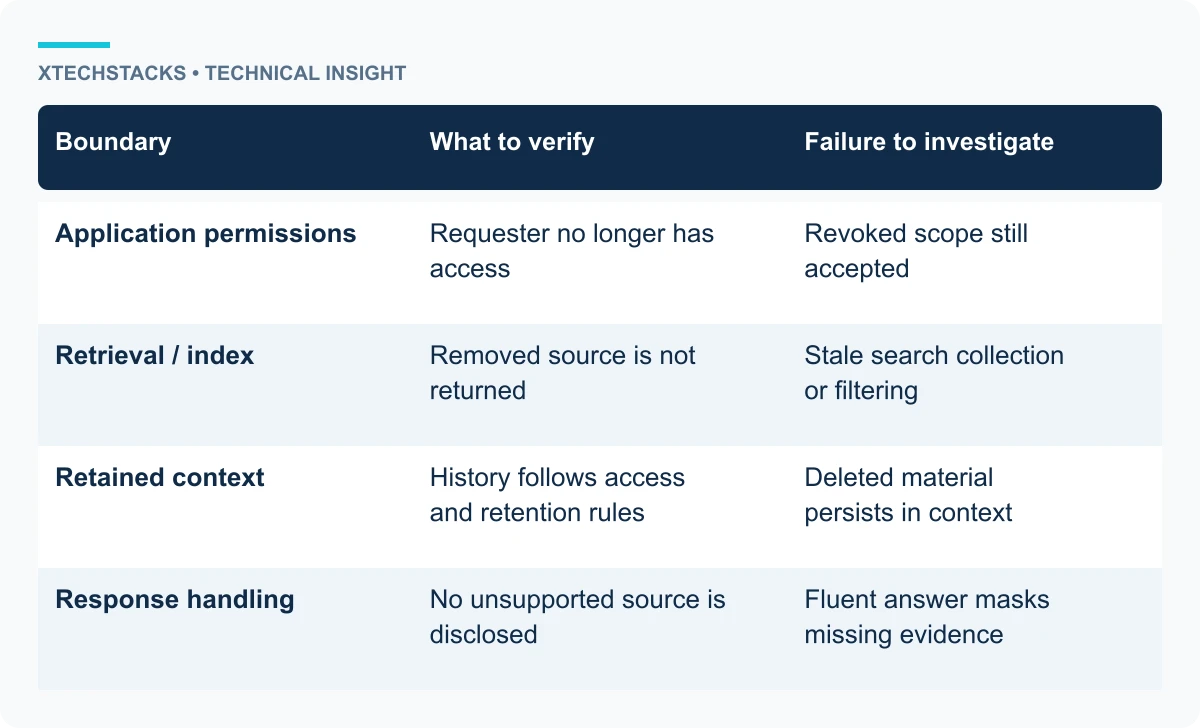
For the documentation example, include tests for revoked access, a deleted document, a provider timeout and a question with no supporting source. Confirm that the user sees an appropriate outcome in each case. These checks are more useful than demonstrating only the happy-path conversation.
Trade-offs and takeaways
This stack can support a modular application, but every integration adds maintenance and observability requirements. Consider whether all four components are necessary for the actual workload. Preserve replaceable boundaries so changing the interface or retrieval service does not require rewriting the permission model.
- Assign one responsibility and owner to each layer.
- Evaluate retrieval and generated answers separately.
- Keep authorization outside prompts and similarity scores.
- Test persistence, provider failures and compatible rollback.
Test source revocation
In an authorized test environment, remove access to one document and repeat a question that previously retrieved it. Verify the retrieval boundary and any retained conversation context. If the document still appears, investigate permissions, index refresh and persistence separately; changing model instructions is not an adequate fix for an access-control defect.