Fast delivery does not remove the need for security review. DevSecOps incorporates security responsibilities into development and operations so that findings can be addressed throughout the delivery lifecycle.
Test at several layers
- Review code and dependencies for known vulnerabilities.
- Scan for accidentally committed credentials.
- Check infrastructure and container configuration.
- Test authentication, authorization and relevant application behavior.
- Perform deeper assessment where the application’s risk warrants it.
Use meaningful release gates
Define how findings are classified, assigned and resolved. A port scan or successful ping is not evidence that an application is secure. Automated checks should support a risk-based decision, not replace it.
Protect access and secrets
Keep credentials out of source code, scripts and build logs. Use scoped access and a managed secret store. Review who can change pipelines or deploy artifacts, and retain an audit trail.
Maintain the process
Assign ownership for remediation, track exceptions and retest changes. Security work continues after deployment as dependencies, threats and configuration change. No single scan guarantees that a service is free from vulnerabilities.
Security is a delivery-system concern
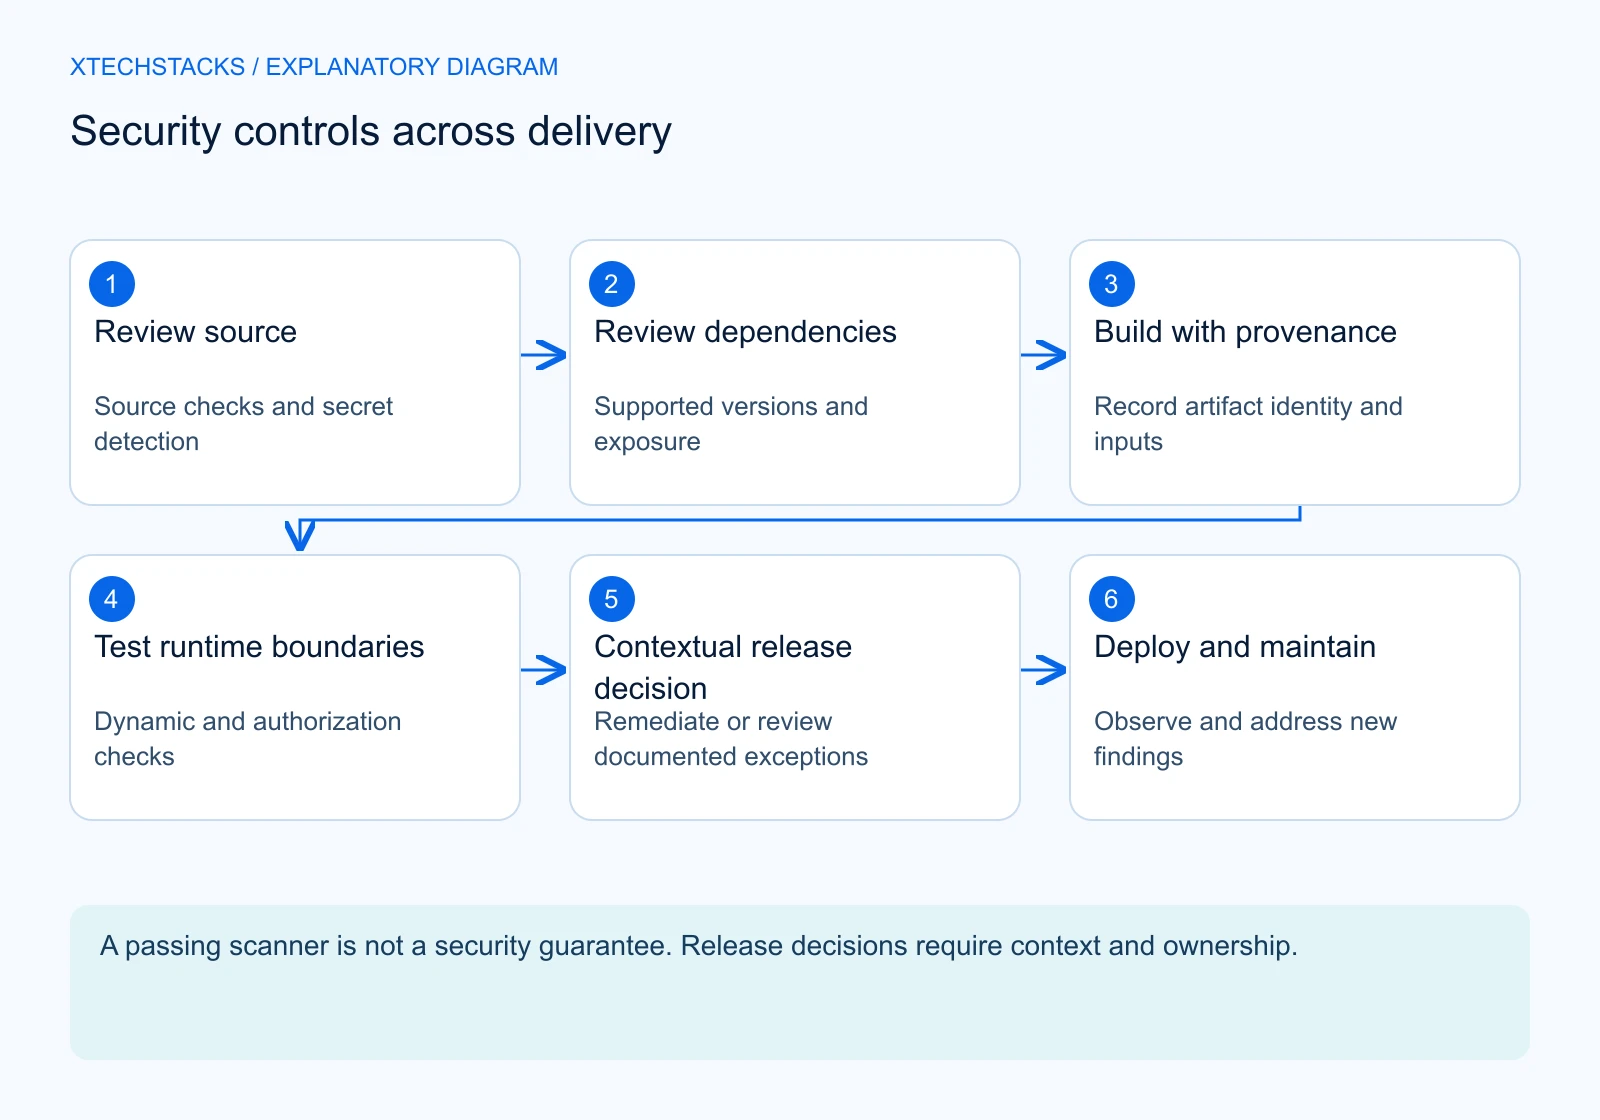
A secure application depends on code, dependencies, build infrastructure, configuration and deployed permissions. Testing one layer does not establish the others. Design controls around the assets and trust boundaries that a release crosses.
For a hypothetical internal API, source review may catch an authorization defect while dependency analysis identifies a vulnerable package. Deployment review must still verify that the service identity and network exposure are appropriate. Each check contributes different evidence.
Source and dependency checks
Static analysis can help identify certain code patterns without executing the application. Dependency analysis can flag known issues in included packages. Results require review in the context of actual use and reachable behavior; a scanner finding is not a complete risk assessment.
Keep dependency versions identifiable and maintain a remediation owner. Pinning a dependency supports reproducibility but does not remove the need to update it. Document exceptions with their scope and rationale rather than allowing unresolved findings to become invisible.
Build integrity and secrets
Restrict who can modify release jobs and access signing or deployment credentials. Separate untrusted contribution checks from privileged release steps. Build scripts are executable code and can cross sensitive boundaries if given broad access.
Scan for accidental secrets where appropriate, but do not rely on scanning as the only protection. Use established secret storage and avoid exposing values in logs or artifacts. If a secret is disclosed, removing it from a file is not sufficient; the affected credential needs the proper incident response.
Dynamic and authorization testing
Test application behavior in an authorized environment with representative identities. Check whether a user can read or modify another user’s resource, whether invalid input is handled safely and whether privileged operations require the intended permission.
Dynamic testing must be scoped to systems the team is authorized to test. A successful scan does not prove the absence of vulnerabilities. Preserve manual review for business rules and access-control conditions that generic scanners may not understand.
Configuration and infrastructure checks
Review deployment definitions for unintended public exposure, broad identities and insecure defaults. Validate relevant image and runtime configuration. Infrastructure automation makes changes reviewable, but a reviewed file can still produce unsafe access if its assumptions are wrong.
Test the resulting deployed state where appropriate. The intended network policy or identity declaration is useful evidence, but operational drift or an integration defect can change its effect. Keep environment-specific exceptions visible and owned.
Release decisions and remediation
Define which findings block a release, who can approve an exception and how remediation is tracked. Severity should account for the affected asset and exposure. Avoid treating every warning equally or suppressing broad categories simply to keep a pipeline green.
When a release proceeds with a known limitation, record the decision and a review date. A temporary exception should not silently become a permanent policy. Retain enough artifact and deployment identity to identify affected releases during an incident.
Trade-offs and recommended approach
Additional checks add execution time and review work. Poorly tuned checks can encourage teams to bypass them. Start with high-value controls tied to actual threats and clear remediation paths, then extend coverage based on incidents and evidence.
Security testing is part of secure development, not a final certification step. Combine it with design review, scoped access, maintenance and response procedures. No article or automated result should be interpreted as declaring an application fully secure.
Key takeaways
- Test code, dependencies, delivery and deployed access separately.
- Protect privileged build and deployment paths.
- Review findings in context and track exceptions.
- Retain artifact identities for incident response.
Test a permission boundary
Create authorized test identities with different roles and attempt a defined cross-account resource access. Verify denial in the backend and inspect the audit record. This concrete check complements scanner output because it evaluates the application’s actual ownership rules and the operational evidence available when a violation is attempted.